Bitcoin Was Changed Forever on This Day 16 Years Ago
Remembering the Day Bitcoin Changed Forever: GPU Mining
U.Today1 min read
Nvidia CEO Jensen Huang stated that China possesses the computing power to train AI models comparable to Anthropic's Claude Mythos, raising concerns for global cybersecurity.
Mentioned in this story
Nvidia CEO Jensen Huang has warned that China already has the computing power and data center capacity necessary to train an AI model at the same level as Anthropic’s AI model Claude Mythos, which could threaten global cybersecurity.
Huang was asked in an interview on the Dwarkesh Patel podcast on Wednesday whether the Chinese government’s access to chips to train a model like Claude Mythos — which has cyberoffensive capabilities — could be a threat to US national security.
Mythos was trained on a “fairly mundane capacity,” Huang said.
“The amount of capacity and the type of compute it was trained on is abundantly available in China, so you just have to first realize that chips exist in China.”
Anthropic limited access to its new AI model in April after it identified thousands of software vulnerabilities across major operating systems and browsers, raising concerns about potential misuse in cyberattacks. A Chinese-made AI model with the same capability could wreak havoc if misused.
Huang said that the amount of compute China has is “enormous.”
“They have datacenters that are sitting completely empty, fully powered. You know, they have ghost cities, they have ghost datacenters too. They have so much infrastructure capacity. If they wanted to, they [could] just gang up more chips.”
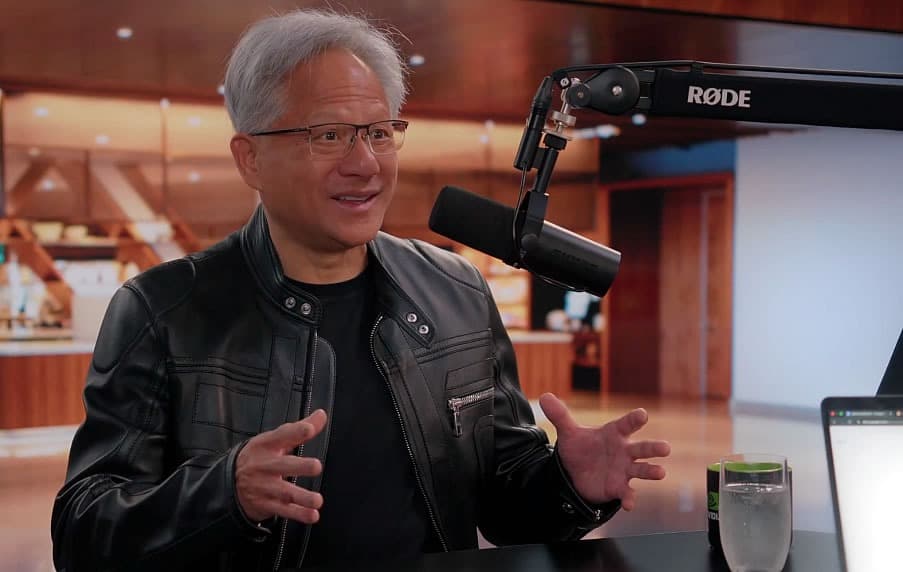
Jensen Huang speaking on China’s AI capacity. Source: Dwarkesh Patel
Huang added that China manufactures 60% of the world’s mainstream chips, has some of the best computer scientists, has 50% of the world’s AI researchers and an abundance of energy.
“Victimizing them, turning them into an enemy, likely isn’t the best answer,” he said. “They are an adversary.”
“We want the United States to win. But I think having a dialogue and having research dialogue is probably the safest thing to do.”
Jensen Huang warned that China has the necessary computing power and data center capacity to train AI models like Anthropic's Claude Mythos.
A Chinese AI model with cyberoffensive capabilities could pose significant risks to US national security if misused.
Anthropic identified thousands of software vulnerabilities across major operating systems and browsers, prompting concerns about potential misuse in cyberattacks.
Remembering the Day Bitcoin Changed Forever: GPU Mining
Bitcoin's network faces a surge of 200,000 fake nodes, raising alarm over a possible stealth Sybil attack.
BTC ETFs led with $622.75 million inflow last week despite net outflows.
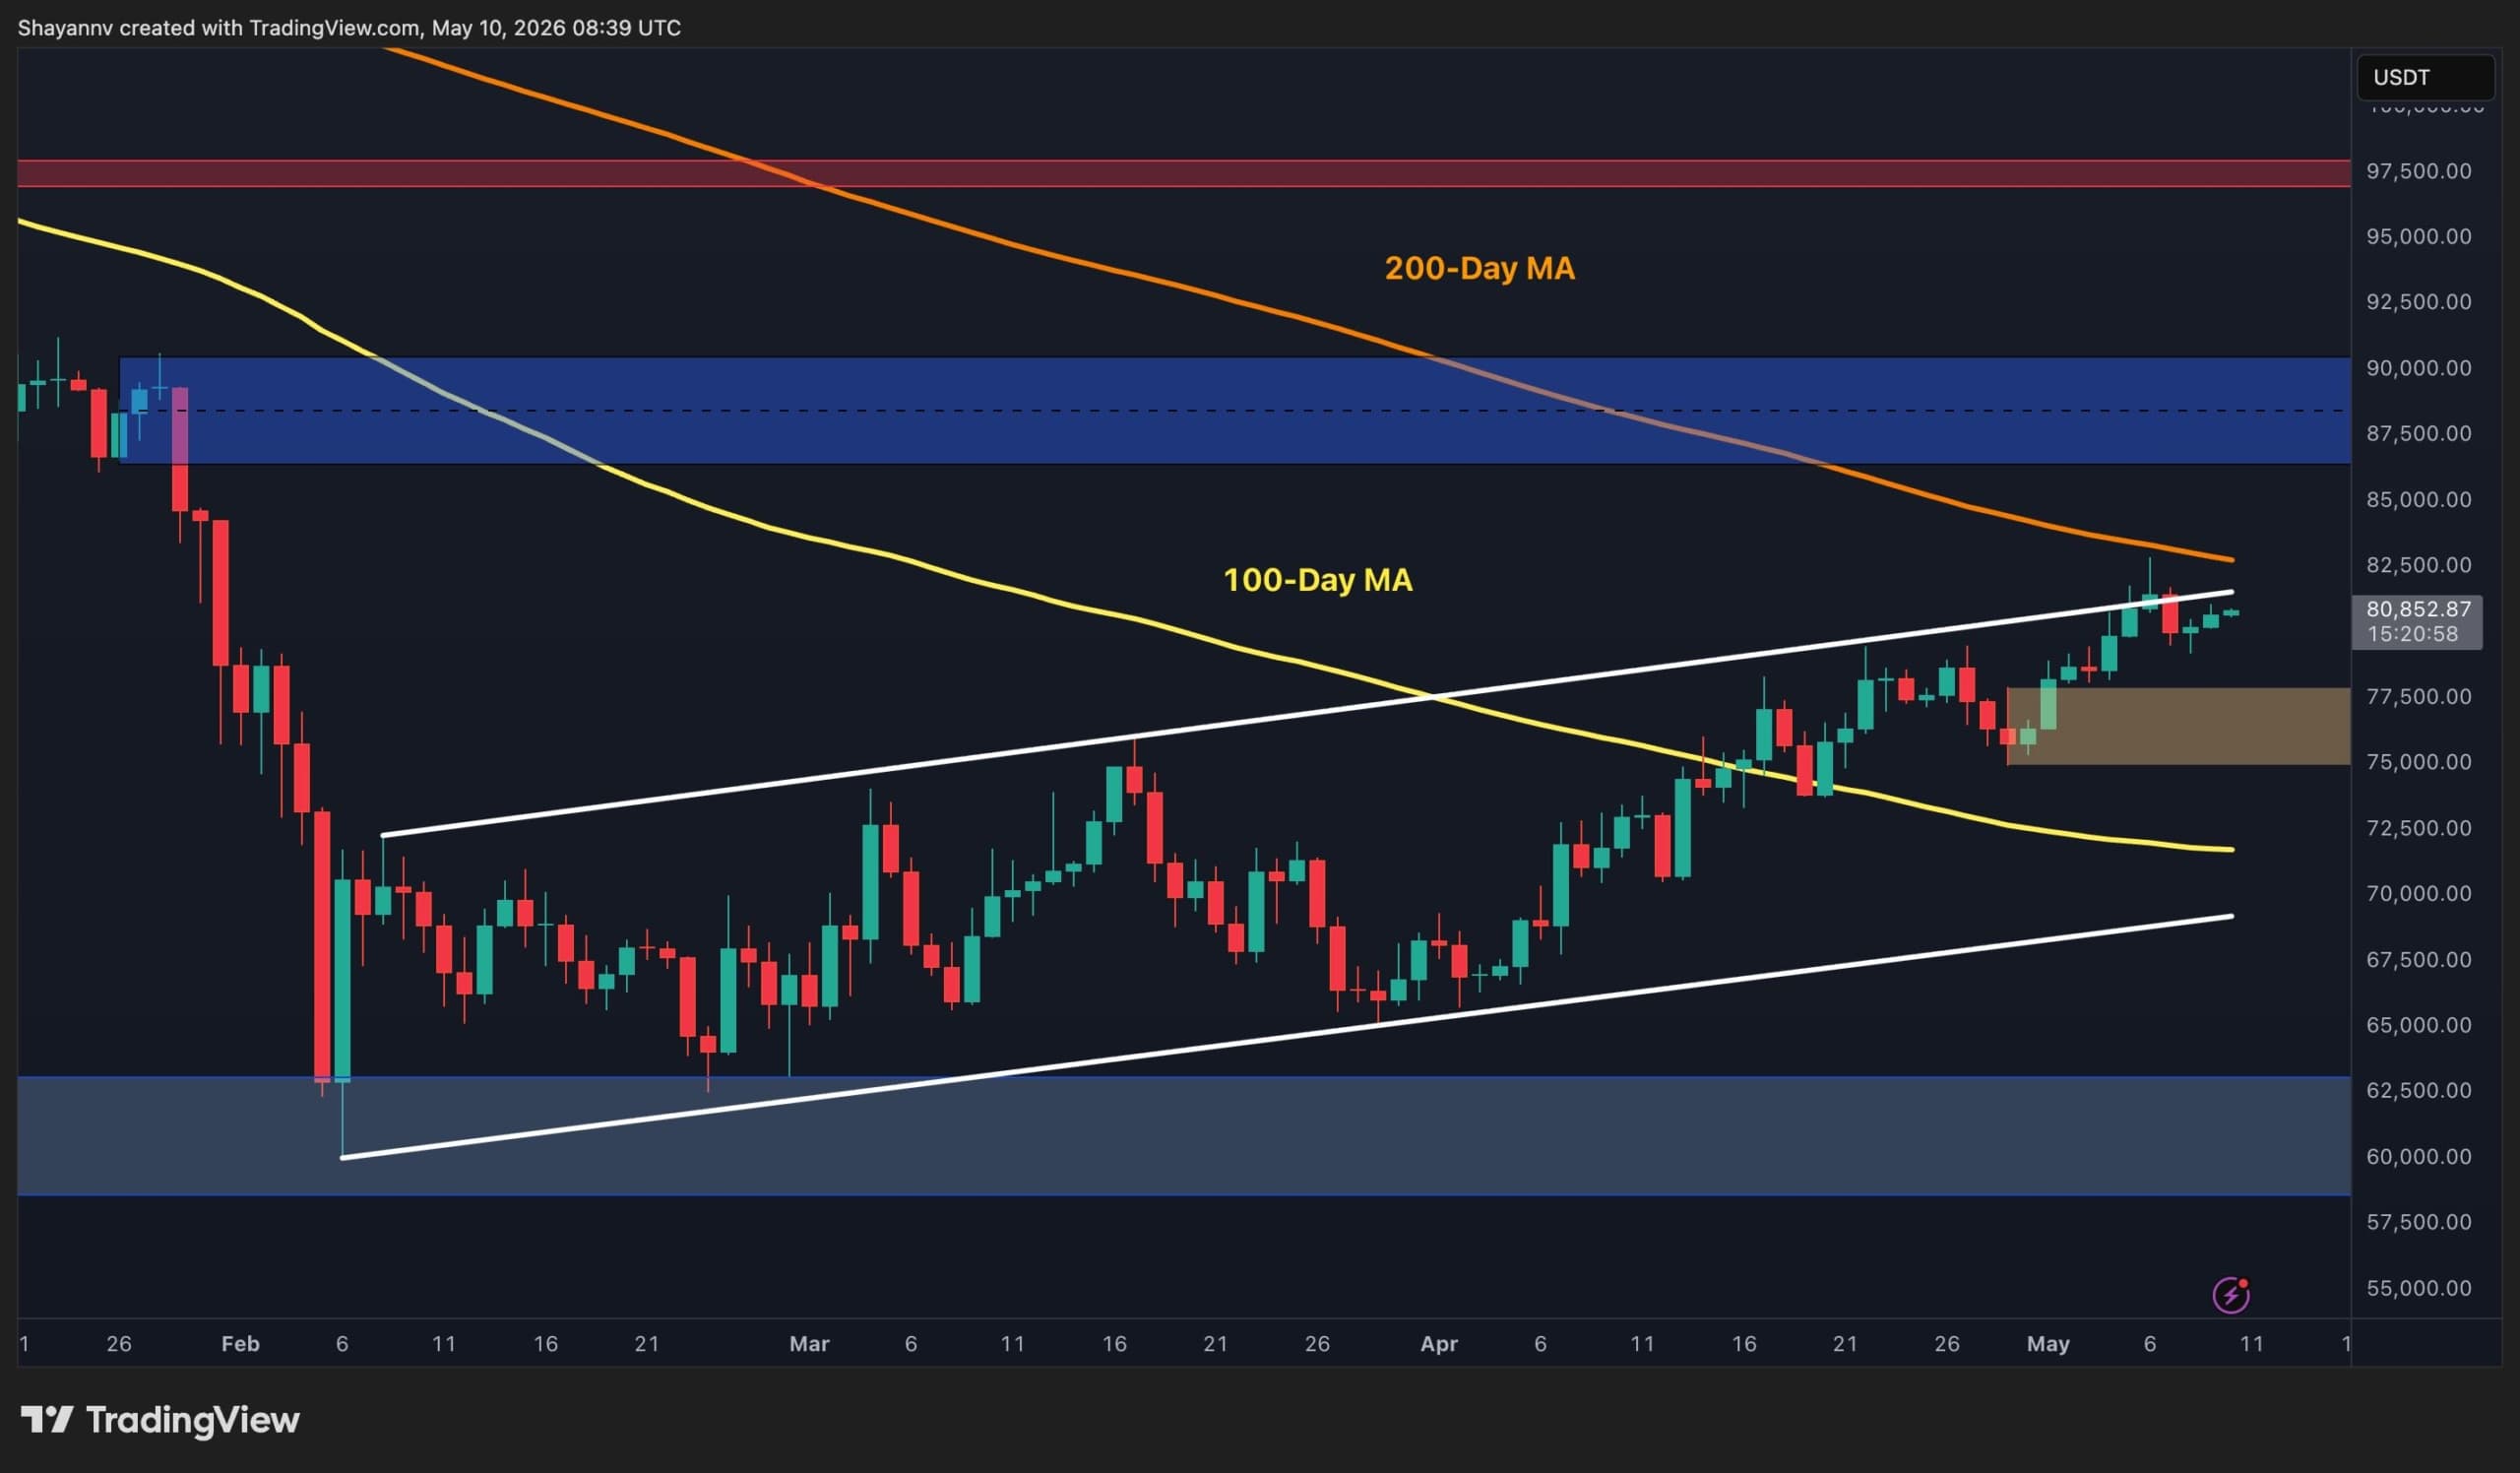
Bitcoin's price struggles at $80K resistance; what to expect next week?
Nearly 80% of Bitcoin is now held by long-term holders, reducing supply for trading.

Google and PayPal leaders discuss the future of commerce on crypto rails at Consensus Miami.
See every story in Crypto — including breaking news and analysis.
On Tuesday, US Treasury Secretary Scott Bessent hailed Mythos as a revolutionary step that will keep America ahead of China in the AI race. “This Anthropic Mythos model was a step function change in abilities, learning capabilities,” he said, according to Bloomberg.
Anthropic released findings on Claude Mythos Preview on April 7, sparking concern that the model could be used in cyberattacks due to its ability to discover and potentially exploit zero-day vulnerabilities. The company also claimed that 99% of the vulnerabilities the model discovered have not been patched yet.
Meanwhile, the AI Security Institute (AISI) evaluated Mythos on April 13, finding that the AI model could “execute multi-stage attacks on vulnerable networks and discover and exploit vulnerabilities autonomously,” tasks that would take human professionals days of work.
AI-boosted hacks with Mythos could also have dire consequences for banks, which often use decades-old software, Reuters reported on Tuesday.
Last year, Anthropic reported in November that a “Chinese state-sponsored group” manipulated its Claude Code tool in an attempt to infiltrate about 30 global targets and succeeded in a small number of cases.