Analyst Predicts Biggest Bitcoin Bull Trap Of The Cycle, Calls Out 50% Crash To $42,000
Analyst warns of a Bitcoin bull trap, predicting a drop to $42,000.
NewsBTC1 min read
A new macOS malware linked to the Lazarus Group targets crypto and fintech firms. The malware, named 'Mach-O Man', is distributed through social engineering tactics, leading to potential financial losses and data exposure.
Mentioned in this story
Security researchers have linked a new macOS malware campaign to the Lazarus Group, the North Korea-linked hacking operation behind some of the crypto industry’s biggest thefts.
Flagged on Tuesday, the new “Mach-O Man” malware kit is distributed via “ClickFix” social engineering schemes across traditional businesses and crypto companies, according to Mauro Eldritch, offensive security expert and founder of threat intelligence company BCA Ltd.
Victims are lured into a fake Zoom or Google Meet call where they are prompted to execute commands that download the malware in the background, allowing attackers to bypass traditional controls without detection to gain access to credentials and corporate systems, the security researcher said in a Tuesday report.
Researchers said the campaign can lead to account takeovers, unauthorized infrastructure access, financial losses and the exposure of critical data, underscoring how Lazarus continues to expand its targeting beyond crypto-native companies.
The Lazarus Group is the main suspect in some of the largest-ever cryptocurrency hacks, including the $1.4 billion hack of Bybit exchange in 2025, the industry’s largest so far.
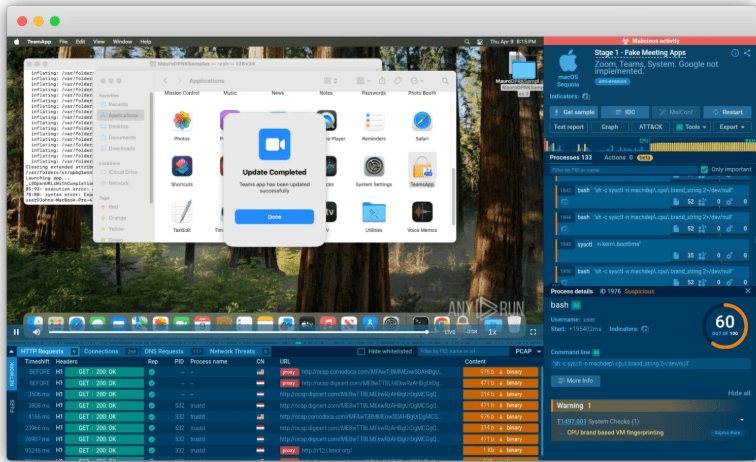
Fake Mach-O Man Kit apps. Source: ANY.RUN
The final stage of the campaign is a stealer designed to extract browser extension data, stored browser credentials, cookies, macOS Keychain entries and other sensitive information from infected devices.
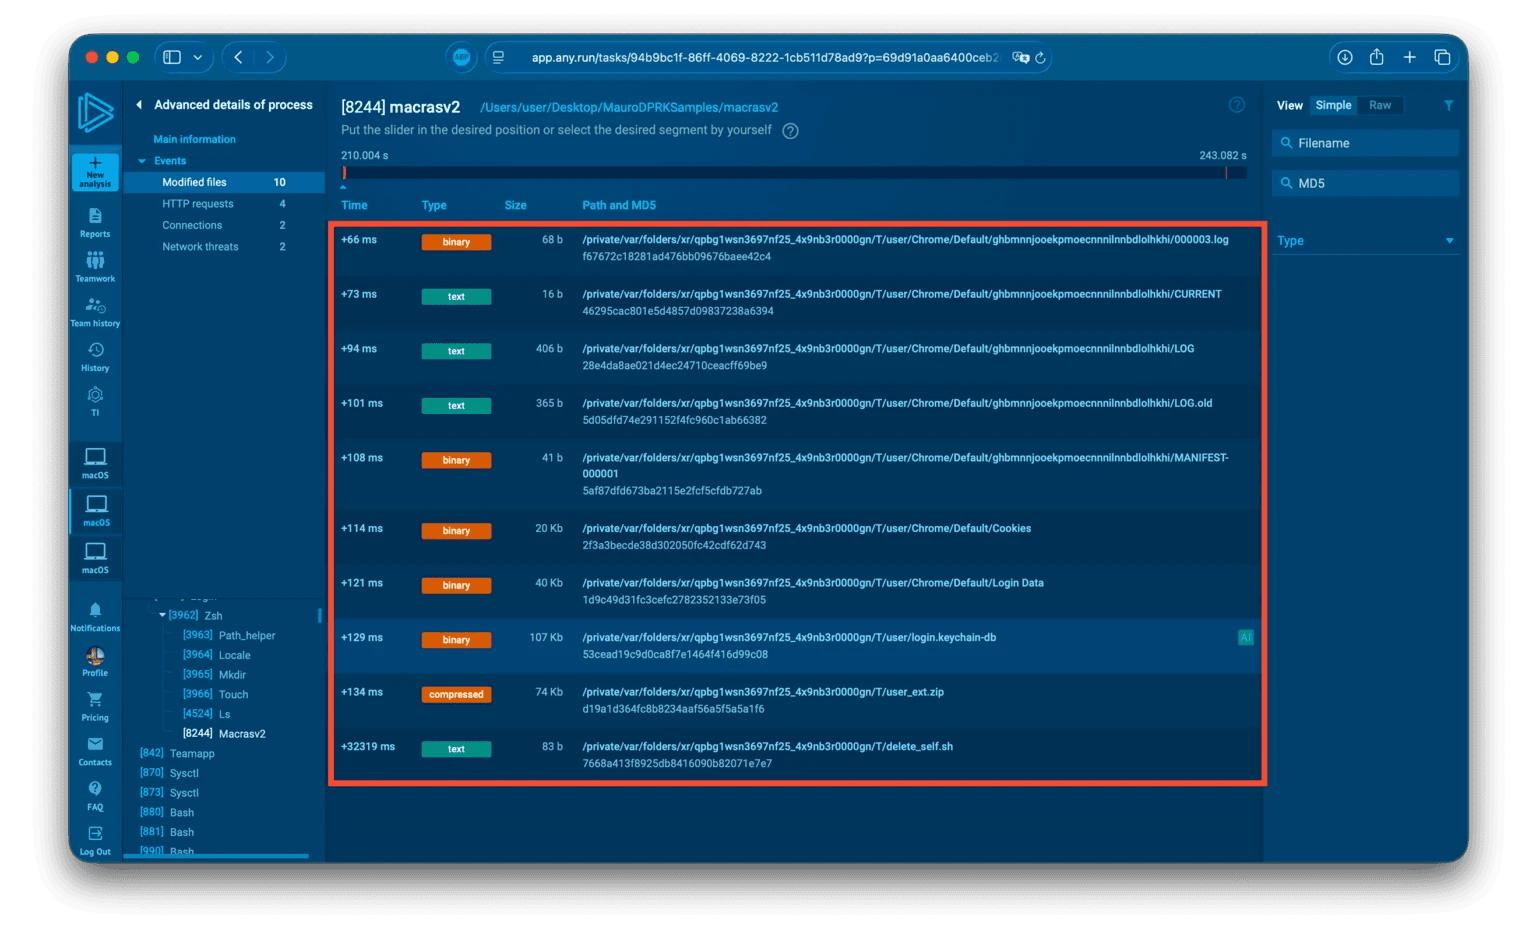
Final staging director for Stealer malware. Source: Any.run
After collection, the data is archived into a zip file and exfiltrated through Telegram to the attackers. Finally, the malware’s self-deletion script removes the entire kit using the system’s rm command, which bypasses user confirmation and permissions when removing files.
The Mach-O Man malware is linked to the Lazarus Group, a North Korea-associated hacking operation.
Victims are lured into fake Zoom or Google Meet calls where they unknowingly execute commands that download the malware.
Consequences include account takeovers, unauthorized access to infrastructure, financial losses, and exposure of critical data.
Analyst warns of a Bitcoin bull trap, predicting a drop to $42,000.

Bitcoin could drop to $60K by Q3 2026 before recovering above $85K.
XRP is coiling for a breakout as it faces key resistance levels. Analysts predict volatility ahead!
Swiss Bitcoin reserve campaign fails, but founder plans another attempt.
American Bitcoin reported an $82 million loss in Q1 2026 despite mining a record 817 BTC. The company's total Bitcoin holdings increased to approximately 7,300 BTC after recent purchases.
XRP Analyst Raises Key Question About Demand in Global Settlement System
See every story in Crypto — including breaking news and analysis.
The novel malware kit was reconstructed by the security expert through cloud-based malware sandbox Any.run’s macOS analysis capabilities.
Earlier in April, North Korean hackers used AI-enabled social engineering schemes to steal about $100,000 worth of funds from crypto wallet Zerion, after gaining access to some team members’ logged-in sessions, credentials and the company’s private keys, Cointelegraph reported on April 15.